In This Article
- What Does It Mean to Hack a Website?
- The Four Main Stages of a Website Attack
- 1. Reconnaissance: Gathering Information About the Website
- Passive Reconnaissance
- Active Reconnaissance
- Common Reconnaissance Tools
- 2. Scanning: Identifying Potential Entry Points
- What Do Hackers Look For During Scanning?
- Common Website Scanning Tools
- 3. Vulnerability Identification: Finding Security Weaknesses
- SQL Injection (SQLi)
- Cross-Site Scripting (XSS)
- Broken Authentication
- Broken Access Control
- Security Misconfiguration
- 4. Exploitation: Testing Whether a Vulnerability Can Be Abused
- Example 1: Broken Access Control
- Example 2: SQL Injection
- Example 3: Cross-Site Scripting
- What Happens After a Successful Exploitation?
- How Can Website Owners Protect Their Websites?
- Where Can Beginners Learn Website Hacking Legally?
- Final Thoughts
Have you ever wondered how hackers break into websites? How does someone discover a website’s weaknesses, gain unauthorized access, or expose sensitive information stored on a server?
Website hacking is often misunderstood as someone typing random commands into a terminal and magically gaining control of a website. In reality, cyberattacks usually involve a series of carefully planned steps, beginning with information gathering and ending with the exploitation of security weaknesses.
Understanding these techniques is an important part of cybersecurity education. It helps aspiring ethical hackers understand how attacks work and teaches website owners how to protect their platforms.
In this guide, we will explore how hackers approach a website, the tools they use, common vulnerabilities they look for, and how organizations defend against these threats.
Note: All practical examples in this article are intended for authorized security testing and educational environments.
What Does It Mean to Hack a Website?
Website hacking involves identifying and exploiting weaknesses in a website’s application, server, database, or underlying infrastructure.
Every website consists of several interconnected components:
- Frontend: The interface visitors interact with, including buttons, forms, and pages.
- Backend: The server-side application responsible for processing requests and managing functionality.
- Database: Stores information such as user accounts, passwords, orders, and other records.
- Web server: Software responsible for receiving and responding to website requests.
- Infrastructure: Hosting servers, networks, cloud services, and other supporting systems.
Each component can introduce potential security weaknesses.
For example, imagine an online shopping website that allows customers to view their orders. If the application does not properly verify account ownership, one customer might be able to access another customer’s order information.
This is an example of a broken access control vulnerability.
The important thing to understand is that hackers don’t necessarily attack the homepage. They investigate the different components that make a website function.
The Four Main Stages of a Website Attack
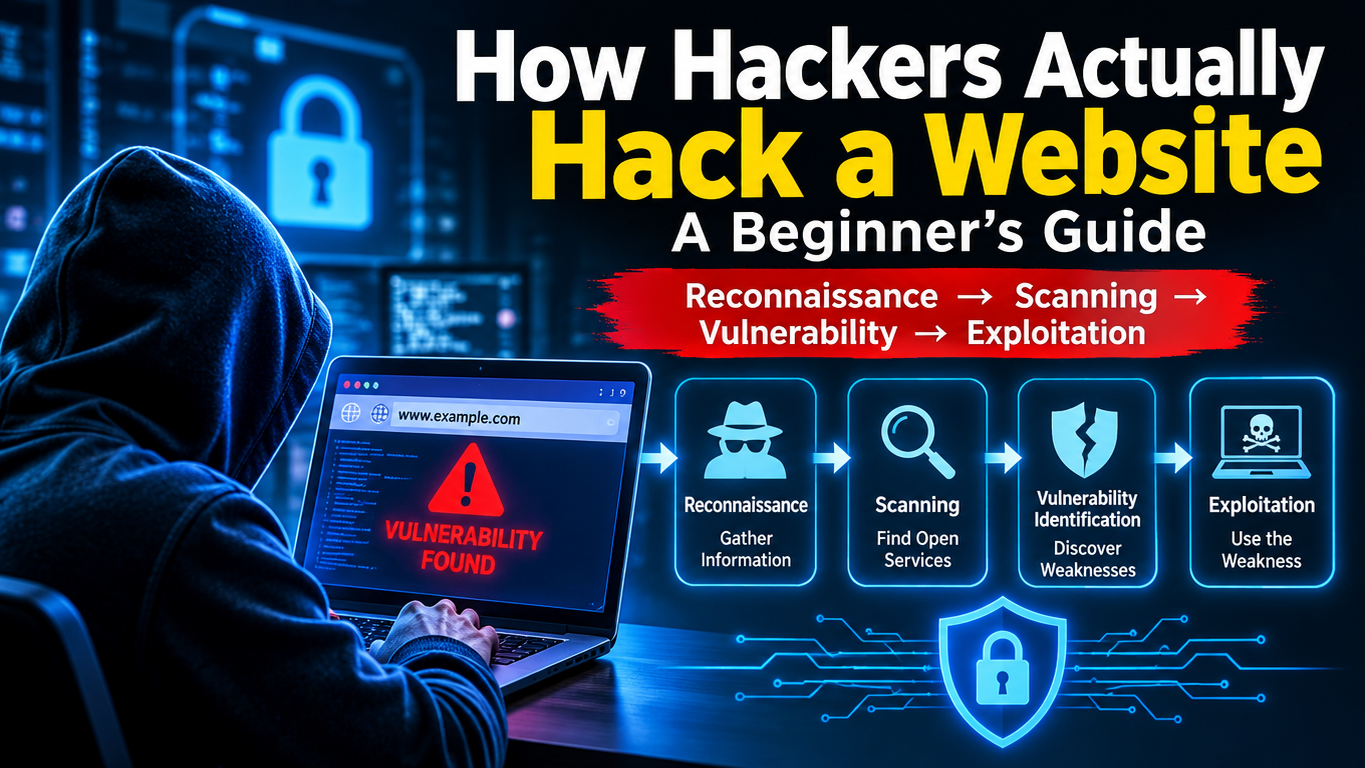
A typical website attack can be divided into four major stages:
- Reconnaissance: Gathering information about the target.
- Scanning: Identifying accessible services and potential entry points.
- Vulnerability identification: Discovering security weaknesses.
- Exploitation: Testing whether those weaknesses can be abused.
These stages are not always performed in a fixed order. Attackers may revisit earlier stages as they discover new information.
Let’s examine each stage.
1. Reconnaissance: Gathering Information About the Website
Reconnaissance is generally the first stage of a website security assessment.
Before attempting to identify vulnerabilities, a hacker needs to understand the target. This involves collecting information about the website, its technologies, publicly accessible resources, and infrastructure.
Think of it as researching a building before conducting a security inspection. You would first learn about its layout, entrances, and security arrangements.
In cybersecurity, this information-gathering process is known as reconnaissance.
Passive Reconnaissance
Passive reconnaissance involves collecting publicly available information without directly probing the target’s systems.
Some examples include:
- Checking domain registration information.
- Discovering publicly available DNS records.
- Searching for indexed files and documents.
- Identifying technologies used by a website.
- Examining publicly available GitHub repositories.
- Reviewing publicly disclosed security incidents.
For example, a researcher investigating a company’s website might discover that it uses WordPress, operates multiple subdomains, and has publicly accessible documentation describing its technology stack.
This information helps build an understanding of the website’s environment.
Active Reconnaissance
Active reconnaissance involves directly interacting with the target’s infrastructure.
Examples include:
- Checking which services respond.
- Inspecting HTTP responses.
- Identifying accessible endpoints.
- Examining exposed services within an authorized testing scope.
Unlike passive reconnaissance, active reconnaissance can generate activity in security logs and trigger monitoring systems.
Common Reconnaissance Tools
Some commonly used tools include:
- WHOIS: Provides domain registration information.
- Shodan: Helps discover internet-connected devices and services.
- Wappalyzer: Identifies technologies used by websites.
- crt.sh: Allows researchers to explore publicly logged SSL certificates.
- DNS lookup tools: Help investigate domain name records.
Reconnaissance matters because publicly exposed information can sometimes reveal outdated software, forgotten subdomains, or incorrectly configured services.
2. Scanning: Identifying Potential Entry Points
After gathering initial information, the next stage is scanning.
Scanning helps security professionals identify accessible services, running applications, and potential weaknesses in a website’s infrastructure.
For example, a company might operate a public website, an administrative dashboard, an API, and a development environment.
Each component needs to be examined to determine whether it is properly secured.
What Do Hackers Look For During Scanning?
Open Ports
Ports are communication endpoints through which applications and services exchange information.
Some commonly encountered ports include:
- Port 80 – HTTP
- Port 443 – HTTPS
- Port 22 – SSH
- Port 21 – FTP
- Port 3306 – MySQL
An open port does not automatically indicate a vulnerability. It simply means a service is accessible through that port.
Running Services
Security professionals identify which software is running behind accessible services.
For example, a web server might use Apache or Nginx. Identifying software versions can help determine whether outdated or vulnerable components are being used.
Subdomains
Large organizations often operate multiple subdomains, such as:
- www.example.com
- admin.example.com
- api.example.com
- dev.example.com
- staging.example.com
Development and staging environments sometimes receive less security attention than production websites.
Directories and Endpoints
Web applications contain different pages and endpoints, such as login pages, dashboards, administrative sections, and APIs.
Security assessments examine whether these endpoints expose information or functionality that should be restricted.
Common Website Scanning Tools
- Nmap: Used for network discovery and service identification.
- Nessus: Helps identify known security vulnerabilities.
- OpenVAS: An open-source vulnerability assessment solution.
- Nikto: Performs web server security checks.
- Burp Suite: Allows security professionals to inspect and test web application traffic.
These tools help identify potential problems, but their results must be reviewed carefully. Automated scanners can produce false positives and may miss complex vulnerabilities.
3. Vulnerability Identification: Finding Security Weaknesses
This is one of the most important stages of a website security assessment.
A vulnerability is a weakness in software, application design, or system configuration that could affect security.
Some vulnerabilities allow unauthorized access, while others expose sensitive information or make applications unavailable.
Here are some common website vulnerabilities.
SQL Injection (SQLi)
SQL injection occurs when an application improperly handles user input that becomes part of a database query.
Imagine a website with a login form. A visitor enters a username and password, and the application checks the credentials against its database.
If developers construct database queries unsafely, specially crafted input might change the meaning of the database query.
Potential consequences include unauthorized access, exposure of sensitive database information, and modification or deletion of records.
How developers prevent it:
- Use parameterized queries.
- Avoid unsafe dynamic SQL construction.
- Apply least-privilege database permissions.
- Handle database errors securely.
Cross-Site Scripting (XSS)
Cross-Site Scripting occurs when a website handles untrusted content in a way that allows unwanted JavaScript execution in another visitor’s browser.
Imagine a website with a comment section. A visitor submits malicious content, and the website displays it without appropriate protection.
When another visitor views the affected page, the browser might interpret that content as executable code.
Potential consequences include unauthorized actions, exposure of information accessible to browser scripts, and manipulation of website content.
How developers prevent it:
- Apply context-aware output encoding.
- Sanitize untrusted HTML.
- Implement Content Security Policy.
- Avoid unsafe DOM manipulation.
Broken Authentication
Authentication is the process of verifying a user’s identity.
Poorly implemented authentication systems can allow attackers to gain access to accounts they do not own.
Common problems include:
- Weak password requirements.
- Insecure password reset mechanisms.
- Poor session management.
- Missing multi-factor authentication.
- Predictable or improperly protected session identifiers.
Developers can reduce these risks through secure password hashing, multi-factor authentication, rate limiting, and properly configured session cookies.
Broken Access Control
Broken access control occurs when an application fails to properly enforce what a user is allowed to access.
Consider an online shopping platform. A customer should only be able to access their own orders.
If the application allows one customer to view another customer’s private order information, it has an access-control vulnerability.
This can happen even when users successfully authenticate.
Prevention methods include:
- Verify permissions on the server for every sensitive request.
- Enforce ownership checks.
- Apply role-based access control.
- Never rely exclusively on hiding buttons or links in the frontend.
Security Misconfiguration
Not every website vulnerability originates in application code. Sometimes, the problem is how the server or application has been configured.
Examples include:
- Default administrator credentials.
- Publicly accessible database services.
- Debug mode enabled on production servers.
- Exposed configuration files.
- Unnecessary services.
- Missing security headers.
Regular configuration audits and secure deployment practices help reduce these risks.
4. Exploitation: Testing Whether a Vulnerability Can Be Abused
Finding a vulnerability and successfully exploiting it are two different things.
Exploitation involves using a security weakness to demonstrate its actual impact.
In professional penetration testing, this process must remain within an explicitly authorized scope.
Let’s understand it through some examples.
Example 1: Broken Access Control
Imagine an online shopping application with two test accounts.
Account A belongs to Customer A, while Account B belongs to Customer B.
Customer A should not be able to access Customer B’s order information.
During an authorized assessment, a security tester checks whether the server correctly verifies ownership of each order.
If the server returns another customer’s information instead of denying access, the tester has demonstrated an access-control vulnerability.
Example 2: SQL Injection
Imagine a developer has created a login system using unsafe database query construction.
A security tester reviews the application’s behavior in a controlled environment and confirms that user input is being interpreted as part of a database command.
The tester documents the issue without accessing or modifying real customer records.
The developer then replaces unsafe query construction with parameterized queries.
Example 3: Cross-Site Scripting
A tester uses a deliberately vulnerable application to demonstrate that untrusted content can be interpreted as executable browser code.
The issue is verified using a harmless proof of concept in a controlled environment.
The developer then implements appropriate output encoding and sanitization.
A responsible security assessment should use the minimum testing necessary to demonstrate impact. Accessing private data or disrupting production services is not necessary to prove most vulnerabilities.
What Happens After a Successful Exploitation?
If an attacker successfully exploits a vulnerability, the consequences depend on the weakness and the privileges obtained.
Some possible outcomes include:
Data Theft: Attackers may gain access to confidential information, including personal details and business records.
Account Takeover: Attackers may gain control of accounts belonging to legitimate users.
Website Defacement: An attacker may modify the content displayed on a website.
Server Compromise: A security weakness might allow unauthorized control over server resources.
Malware Deployment: A compromised environment might be used to distribute malicious software.
Service Disruption: Attackers may interfere with website availability, preventing legitimate visitors from accessing it.
In serious incidents, attackers may also attempt to maintain unauthorized access or move between compromised systems.
This is why detecting suspicious activity early is just as important as preventing the initial vulnerability.
How Can Website Owners Protect Their Websites?
Understanding how attackers operate is only half of cybersecurity. The other half is knowing how to defend against these threats.
Website owners and developers should follow these security practices:
- Keep WordPress, plugins, themes, and server software updated.
- Use strong and unique administrator passwords.
- Enable multi-factor authentication.
- Use HTTPS with a valid SSL/TLS certificate.
- Configure a firewall and appropriate security rules.
- Regularly scan for known vulnerabilities.
- Restrict database and administrative access.
- Use secure coding practices and parameterized SQL queries.
- Maintain regular and tested backups.
- Monitor server logs and suspicious login attempts.
- Remove unused plugins, themes, and services.
- Apply least-privilege permissions to users and applications.
Security should be treated as an ongoing process rather than a one-time configuration.
Where Can Beginners Learn Website Hacking Legally?
You don’t need to attack real websites to understand how cybersecurity works.
Several platforms provide deliberately vulnerable applications and controlled environments where beginners can practice ethical hacking.
1. OWASP Juice Shop
A deliberately insecure web application designed to teach common web security vulnerabilities.
Website: https://owasp.org/www-project-juice-shop/
2. PortSwigger Web Security Academy
Provides free interactive lessons and practical labs covering SQL injection, XSS, authentication, access control, and other web security topics.
Website: https://portswigger.net/web-security
3. TryHackMe
Offers beginner-friendly guided cybersecurity rooms and hands-on exercises.
Website: https://tryhackme.com/
4. Hack The Box
Provides practical cybersecurity challenges and penetration-testing environments for learners at different skill levels.
Website: https://www.hackthebox.com/
These platforms allow learners to develop practical skills without targeting real organizations.
Final Thoughts
Website hacking is not simply about finding a password or running a particular command in a terminal. It involves understanding systems, gathering information, identifying weaknesses, and evaluating their potential impact.
Reconnaissance helps build an understanding of the target. Scanning identifies exposed services and application components. Vulnerability identification reveals security weaknesses, while exploitation demonstrates whether those weaknesses can actually compromise a system.
For website owners, understanding these stages can make the difference between reacting to a cyberattack and preventing one before it happens.
As websites become increasingly important to businesses and individuals, cybersecurity knowledge is no longer optional. It is an essential part of operating safely in the digital world.
Remember: Only test websites and systems that you own or have explicit permission to assess. Ethical hacking is about improving security, not compromising someone else’s systems.
Recommended Further Reading
- OWASP Top 10: https://owasp.org/www-project-top-ten/
- OWASP Web Security Testing Guide: https://owasp.org/www-project-web-security-testing-guide/
- NIST Technical Guide to Information Security Testing: https://csrc.nist.gov/pubs/sp/800/115/final

Leave a Reply